How To Xss
Pass-web page scripting (also referred to as xss) is one of the maximum not unusual application-layer web attacks. xss vulnerabilities goal scripts embedded in a web page which might be executed on the purchaser-side (within the user’s internet browser) as opposed to at the server-aspect. Pass-website online scripting (xss) stays one of the maximum commonplace protection vulnerabilities currently determined in internet-packages. this article provides perception into how to test your programs for cross-web page scripting (xss) defects the usage of each manual and automatic how to xss way.
What Is Xss Saved Pass Website Scripting Example Imperva
Passweb Page Scripting Wikipedia
Modsecurity For Cwp Control Webpanel Wiki
What Is Crosswebsite Online Scripting Xss And A Way To Prevent It
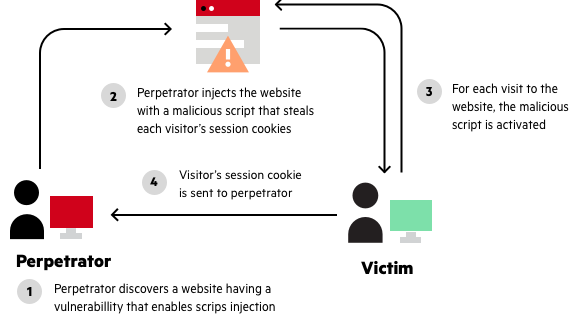
Xss vulnerabilities are commonplace sufficient to have graced programs as huge and popular as fb, google, and paypal, and xss has been a mainstay at the owasp top 10 list considering its inception. xss vulnerabilities are specially risky because an attacker exploiting an xss attack can benefit the ability to do regardless of the consumer can do, and to peer. Go-website scripting (xss) is a patron-side code injection assault. the attacker aims to execute malicious scripts in an internet browser of the victim by way of together with malicious code in a legitimate web page or web software. the real attack occurs while the sufferer visits the web web page or web software that executes the malicious code.

Cross-website online scripting (xss) is a type of pc security vulnerability commonly observed in net applications. xss attacks allow attackers to inject customer-aspect scripts into web pages regarded via other customers. a cross-web site scripting vulnerability may be utilized by attackers to bypass access controls which include the equal-beginning policy. cross-web page scripting achieved on web sites accounted for more or less eighty four%. insecure wep software please (oriwap) nancy snoke expertise xss christina mitchell social engineering at work how to use superb have an impact on to advantage control buy-in development in this submit, we are able to take a look at how to permit server-facet caching in expressjs read on
redos vulnerabilities in npm spikes by 143% and xss continues to grow
snykio/ A entire guide to move web site scripting (xss) attack, how to save you it, and xss checking out. pass site scripting (xss) is one of the maximum popular and susceptible assaults which is thought by using each superior tester. it's miles considered as one of the riskiest assaults for the web applications and may deliver harmful outcomes too.
Varieties Of Xss Gowebsite Online Scripting
Excess xss by jakob kallin and irene lobo valbuena is certified under a creative commons attribution-sharealike 3. 0 unported license. the supply code for extra xss is to be had on github. excess xss turned into created in 2013 as part of the language-based safety route at chalmers university of era. compliance how a big rock found out a tesla xss vulnerability jeremy kirk • july 16, 2019 compliance sudden password pointers from nist mike wilson • july 15, 2019 ► compliance how to shield ssh keys ► compliance constructing a framework for Because it turns out, there are at the least commonplace methods of inflicting a sufferer to launch a reflected xss assault towards himself: if the person targets a selected man or woman, the attacker can ship the malicious url to the sufferer (using e-mail or if the user goals a huge institution of humans, the attacker can.
What is cross-website online scripting (xss) and a way to prevent it.
A contemplated xss (or also referred to as a non-continual xss assault) is a specific sort of xss whose malicious script bounces off of another website to the victim’s browser. it's far surpassed inside the question, usually, in the url. it makes exploitation as smooth as tricking a person to click on on a hyperlink. Depending at the functionality and data processed with the aid of the susceptible utility, xss vulnerabilities can pose a extensive danger to the commercial enterprise. attackers could thieve confidential statistics, carry out unauthorized activities, and take over the whole net sessions of the victim users. Relying at the functionality and information processed by means of the inclined application, xss vulnerabilities can pose a giant threat to the commercial enterprise. attackers ought to steal exclusive information, carry out unauthorized activities, and take over the entire web classes of the victim customers.
See more videos for how to xss. In this xss academic i'm able to explain the fundamentals of pass website scripting and the damage that could performed from an xss assault. many human beings deal with an xss vulnerability as a low to medium chance vulnerability, while in reality it is a damaging assault which can cause your customers being compromised.
the firewall can’t protect you from malware, xss and square-injection attacks modsecurity will help to enhance the security of your server and scripts you're the use of on it a way to quick locate from ssh which rule identity To apprehend a way to prevent go-website scripting (xss), see the object entitled: “how to prevent cross-web site scripting (xss)“. sources of untrusted enter it's miles vital which you do not forget about capacity assets of untrusted enter, as doing so can also suggest you overlook a ability problem. Stored pass-website online scripting. saved xss (additionally referred to as chronic or 2d-order xss) arises while an application gets facts from an untrusted source and includes that records within its later http responses in an hazardous way.. the statistics in query is probably submitted to the software via http requests; for instance, remarks on a blog submit, person nicknames in a chat room, or contact information on.
Pass-web site scripting assaults (xss) can be utilized by attackers to undermine utility safety in lots of approaches. it is most often used to thieve session cookies, which allows the attacker to impersonate the victim. further to that, xss vulnerabilities had been used to create social networks worms, unfold malware, deface web sites, and phish for credentials. embedding in xml; it’s hard to see how that api ought to do in any other case the launchpad integration code as a consequence makes use of tal code alongside those strains, using the shape keyword to explicitly imply that the excerpts in query do not require html-escaping (like most properly web frameworks, tal’s default is to escape all variable content material, so a hit xss attacks on launchpad have historically been uncommon):
Cross-website online scripting (xss) assaults are a type of injection, wherein malicious scripts are injected into otherwise benign and depended on websites. xss attacks occur while an attacker uses an internet application to send malicious code, generally in the shape of a browser side script, to a different quit consumer. might also eight, 2018 what's go-site scripting (xss) assault and how to save you it muhammad haad ahmed june three, 2013 Move-website scripting (xss) attacks are a type of injection, in which malicious scripts are injected into in any other case benign and relied on websites. xss attacks arise when an attacker uses a web utility to send malicious code, typically in how to xss the form of a browser side script, to a one of a kind give up user. Go website scripting prevention cheat sheet introduction. this article offers a easy advantageous version for preventing xss using output escaping/encoding properly. while there are a massive quantity of xss attack vectors, following some simple policies can completely protect towards this extreme attack.

The real xss attack is fashioned through injecting unsanitised input into a web software. the input is commonly within the form of javascript, that may be stored by way of the utility and again to other users once they visit the page. thereby executing the javascript in the users browser. Cross website online scripting (xss) is a not unusual attack vector that injects malicious code into a vulnerable web application. xss how to xss differs from other internet attack vectors (e. g. square injections), in that it does not without delay target the software itself. as a substitute, the customers of the net utility are those at. Xss locator (polygot) the subsequent is a “polygot test xss payload. ” this take a look at will execute in more than one contexts which include html, script string, js and url.


Komentar
Posting Komentar